Synology urges DSM updates after ransomware attacks
Technology · First reported 3 Nov, 07:43 · Updated 08:22

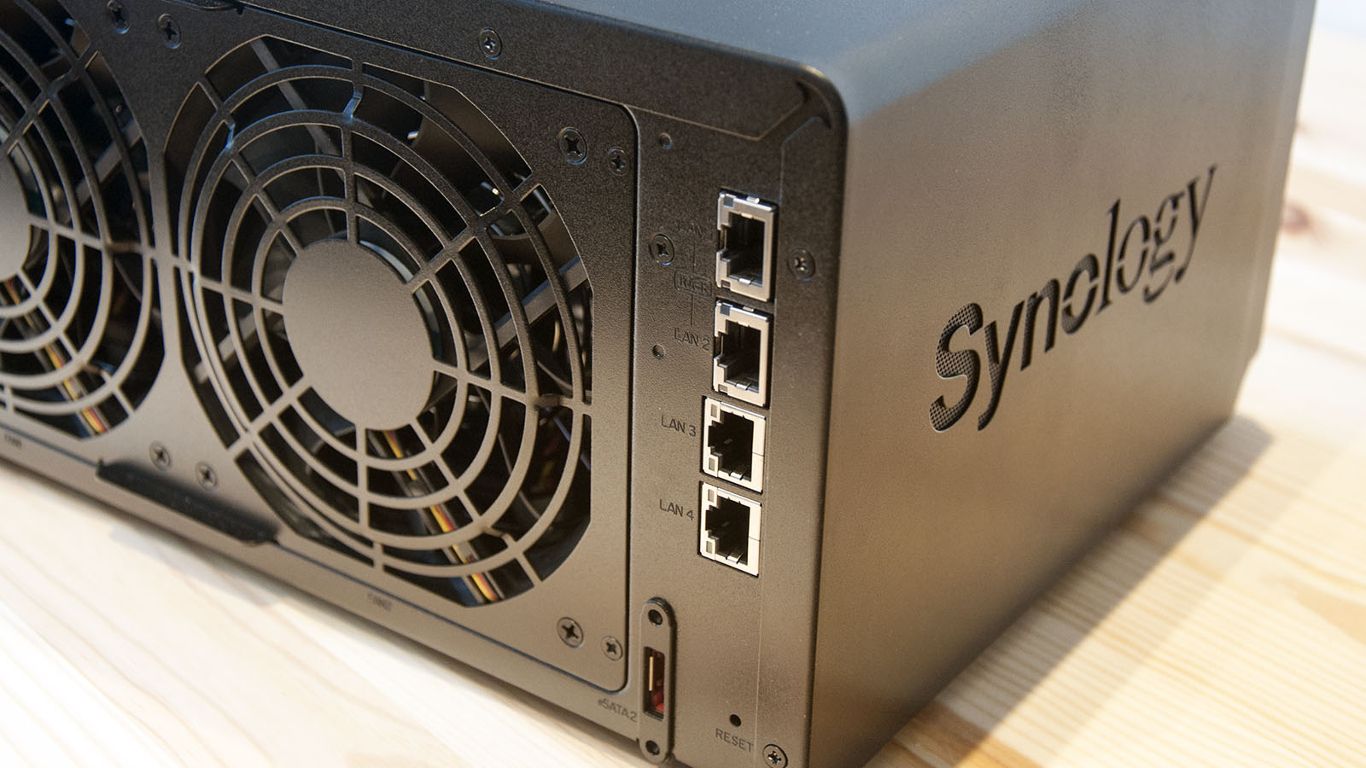
Synology says attackers are targeting devices running outdated DiskStation Manager software. The company urges users to update and enable automatic updates.
- Synology says attackers are exploiting a vulnerability patched in December 2024 to target devices running outdated DSM; it has not identified the exact flaw being used in these attacks.
- Customers have reported C3RB3R ransomware infections on Synology devices. The malware encrypts files with a .L0CK3D extension and leaves a ransom note, according to the report.
- Synology urges users of vulnerable DSM versions to update immediately and recommends enabling automatic updates.
Summary written by Lux AI from 2 articles
Key facts
- Target
- Synology NAS devices running outdated DiskStation Manager software
- Patch timing
- The flaw Synology says attackers are exploiting was patched in December 2024
- Reported ransomware
- C3RB3R; encrypted files receive a .L0CK3D extension
- Company guidance
- Update vulnerable DSM versions immediately and enable automatic updates
Source spectrum
Far left
Left
Lean left
Centre


Lean right
Right
Far right
Left 0 · Centre 2 · Right 0 of 2 rated sources
Images from the coverage
Background
- An earlier report described a ransomware threat involving GMO’s Onamae Desktop Cloud; it said the company urged customers to disconnect systems and shut down computers, and another report said ransomware was not installed on user devices.
- Earlier reports described authorities seizing Virtualine or its domain, which was linked to cybercrime activity; the supplied summaries provided few details about the operation.
All coverage
Coverage over time
LeftCentreRight
Articles per hour since first reported, by side.
Ownership
- Corporation 100% (2)
Share of the 2 sources by owner type.