Fake ChatGPT and Claude downloads reportedly deliver malware
AI · First reported 29 Oct, 14:10 · Updated 15:54

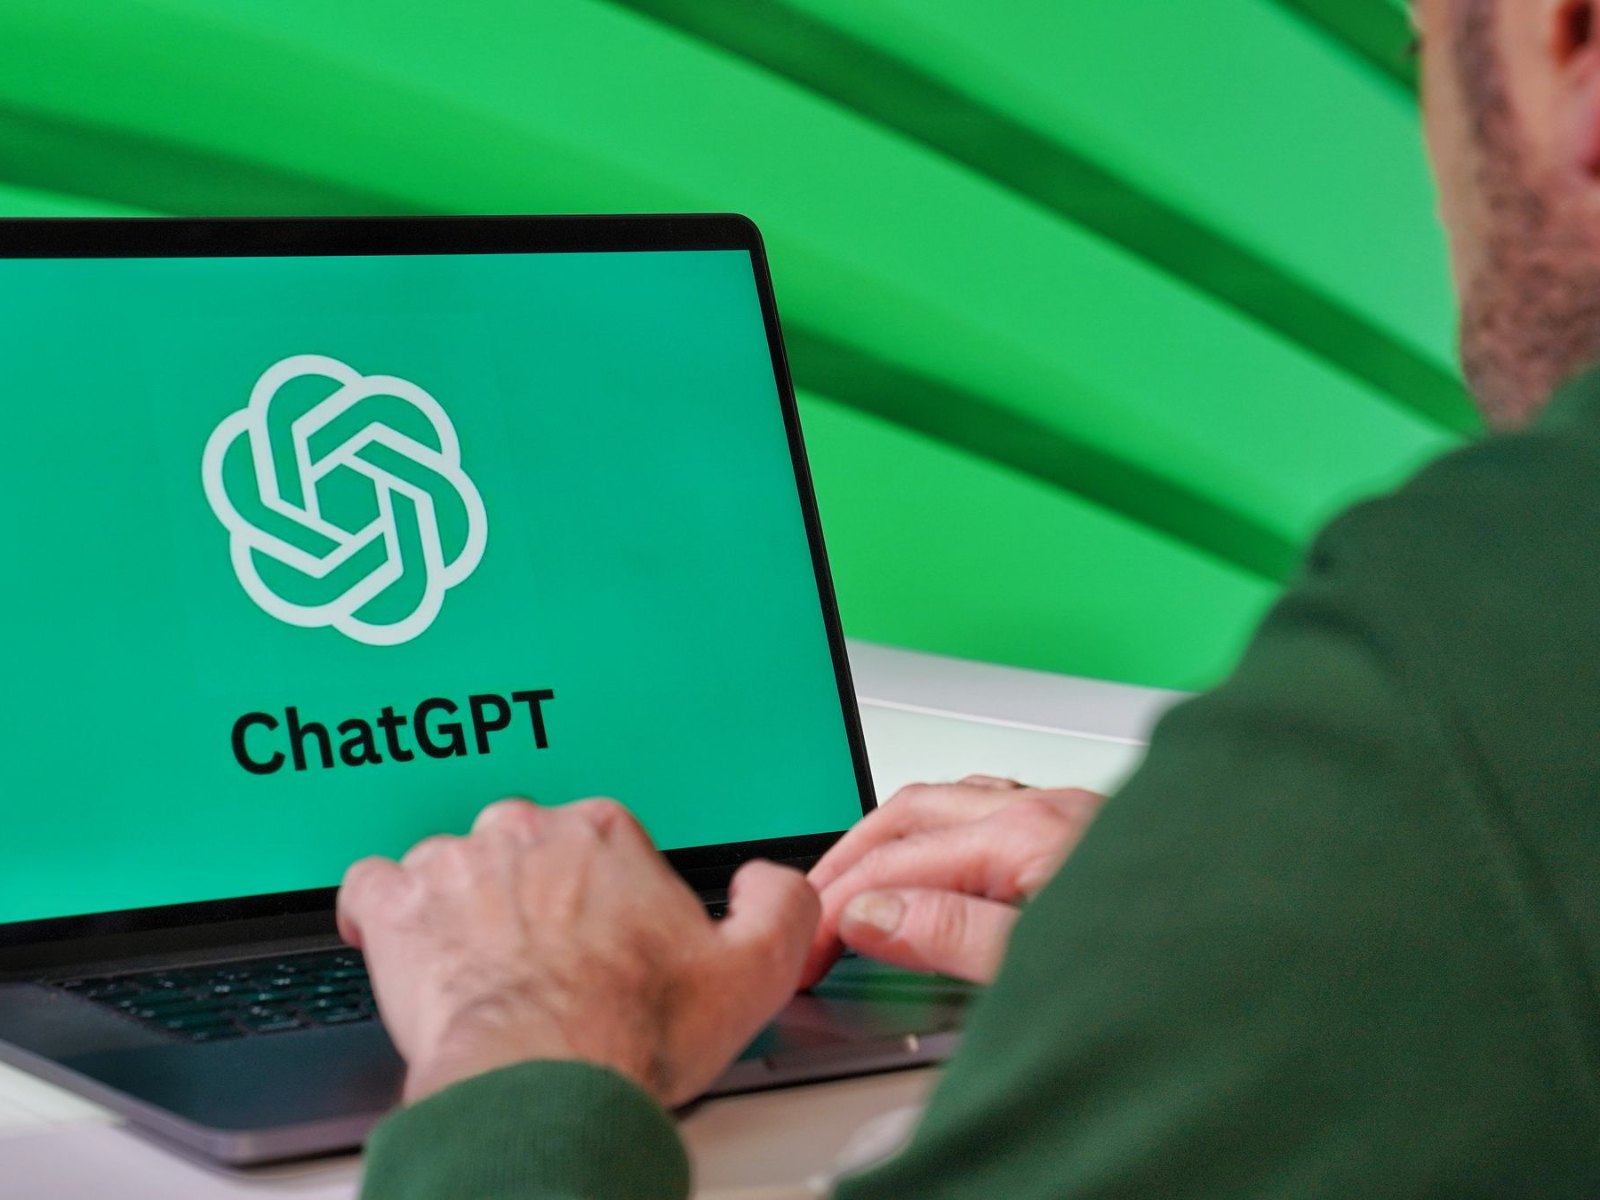
Researchers describe a campaign called Yoba that disguises malicious downloads as desktop apps for ChatGPT and Claude. The reported ZIP files contain genuine signed installers alongside a malicious DLL; running the installer can load the DLL and install a cryptominer.
- Check Point Research says Yoba used fake GitHub projects and landing pages that appeared prominently in Google results.
- The ZIP files reportedly bundled genuine signed installers with a malicious winmm.dll, which could be loaded when the installer ran.
- Check Point observed an XMRig cryptominer as the payload and said the loader could also deliver other malware.
Summary written by Lux AI from 2 articles
Key facts
- Campaign name
- Yoba, as named by Check Point Research.
- Impersonated apps
- ChatGPT and Claude desktop apps.
- Malicious file
- A library named winmm.dll, according to Notebookcheck.
- Observed payload
- XMRig cryptominer, according to Check Point's observation reported by Notebookcheck.
- Tracking period
- About two months, according to Check Point Research as reported by Notebookcheck.
Source spectrum
Far left
Left
Lean left
Centre


Lean right
Right
Far right
Left 0 · Centre 2 · Right 0 of 2 rated sources
Images from the coverage
All coverage
Coverage over time
LeftCentreRight
Articles per hour since first reported, by side.
Ownership
- Corporation 50% (1)
- Unknown 50% (1)
Share of the 2 sources by owner type.